
Hướng Dẫn Sử Dụng
A Guide to Configuring Proxy Chaining to Enhance Network Security

Table of contents
What Is Proxy Chaining?
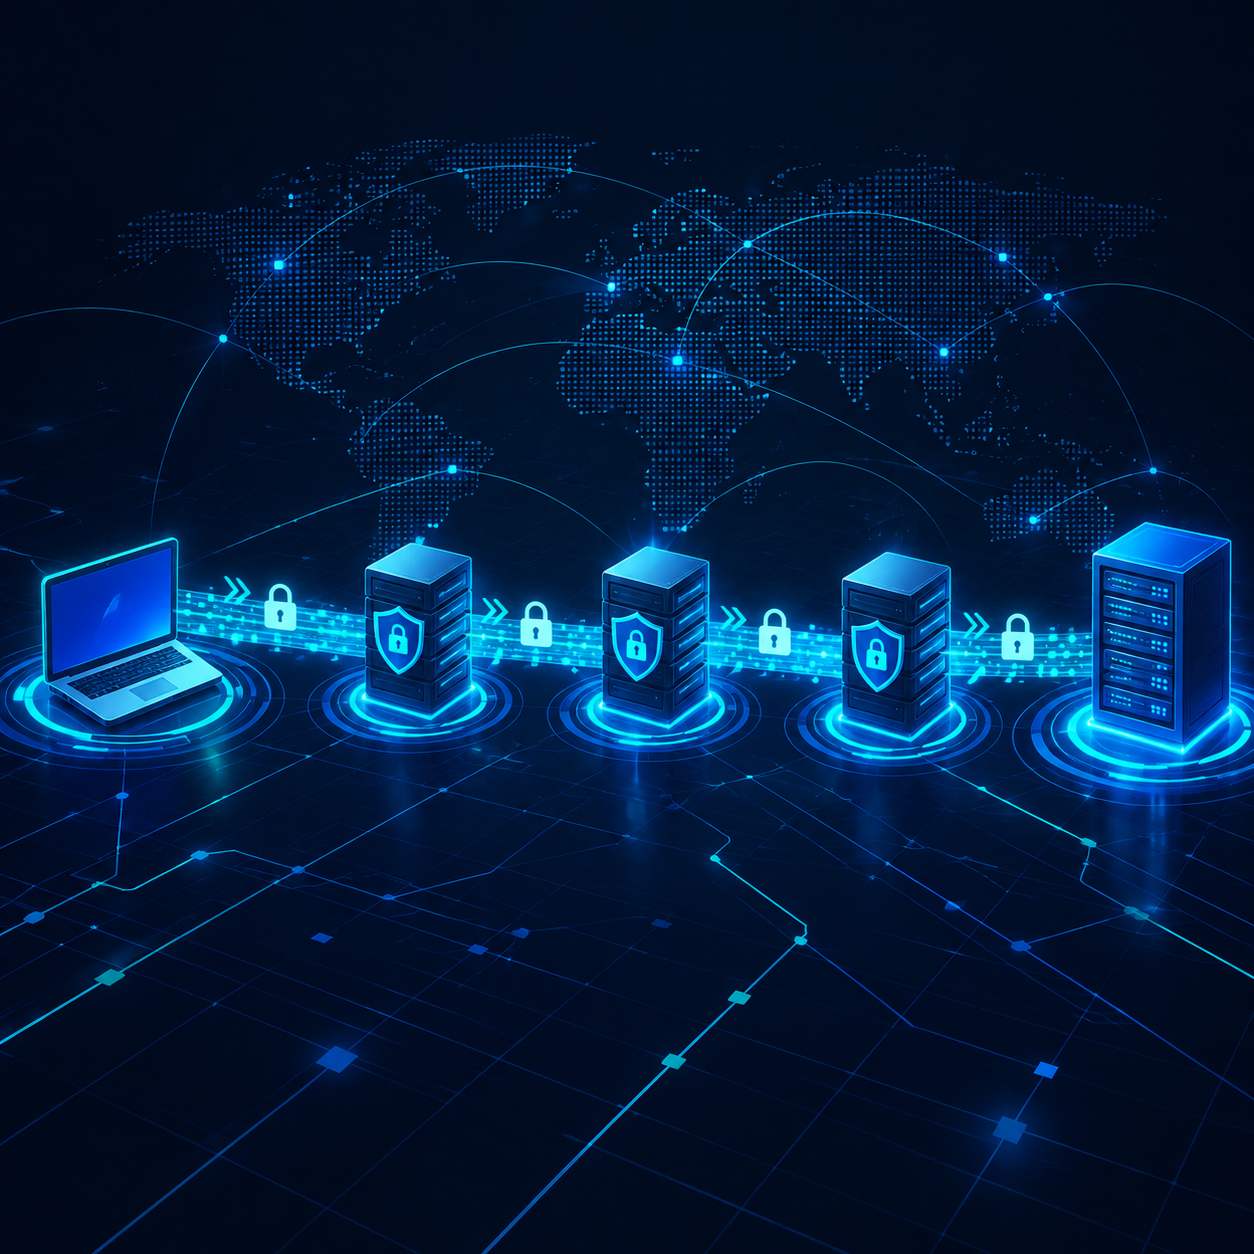
In modern networking environments, the need to protect digital identities and maintain online privacy has become increasingly critical. The proxy chaining technique, also known as establishing a proxy chain, is a method of routing Internet traffic through multiple intermediate servers in succession before reaching the final destination server.
Instead of merely sending requests directly from a client to a single proxy, the nested proxy connection approach creates an intricate path. The client sends data to the first proxy, this server forwards the packets to the second proxy, and so on until the final link establishes the connection with the destination. This model disperses identifiable information, significantly enhancing proxy security.
Benefits of Using a Proxy Chain
Applying a multi-tiered routing model delivers several distinct advantages in managing traffic and strengthening defenses:
- Enhanced Anonymity: The destination server only observes the network address of the final proxy in the list. Even if one link in the chain leaks its access logs, the other links still protect the user's original identity.
- Layered Access Segmentation: Routing across different network partitions supports operations within infrastructures governed by strict monitoring policies, allowing traffic to traverse properly designated service ports.
- Data Transmission Protection: By combining different encryption protocols across intermediate nodes, traffic faces a minimized risk of interception or tampering in transit.
Common Protocols in Nested Proxy Connections
To implement a proxy chaining configuration effectively, administrators must understand the characteristics of the protocols typically combined:
HTTP and HTTPS Proxy Protocols
HTTP proxies operate primarily at the application layer, suitable for standard web page transmission. When upgraded to HTTPS proxies, the connection gains a TLS/SSL security layer, supporting the HTTP CONNECT method to create a secure data tunnel through the intermediate node.
SOCKS Protocol (SOCKS4/SOCKS5)
The SOCKS protocol operates at a lower layer, flexibly handling multiple traffic types such as TCP and UDP without altering packet contents. In particular, SOCKS5 supports user authentication and remote domain name resolution, playing a pivotal role in constructing robust links for a proxy chain.
Detailed Guide to Configuring Proxy Chaining
Below are methods for setting up a multi-proxy model using popular tools in Linux environments and security workstations.
Method 1: Configuring with ProxyChains on Linux
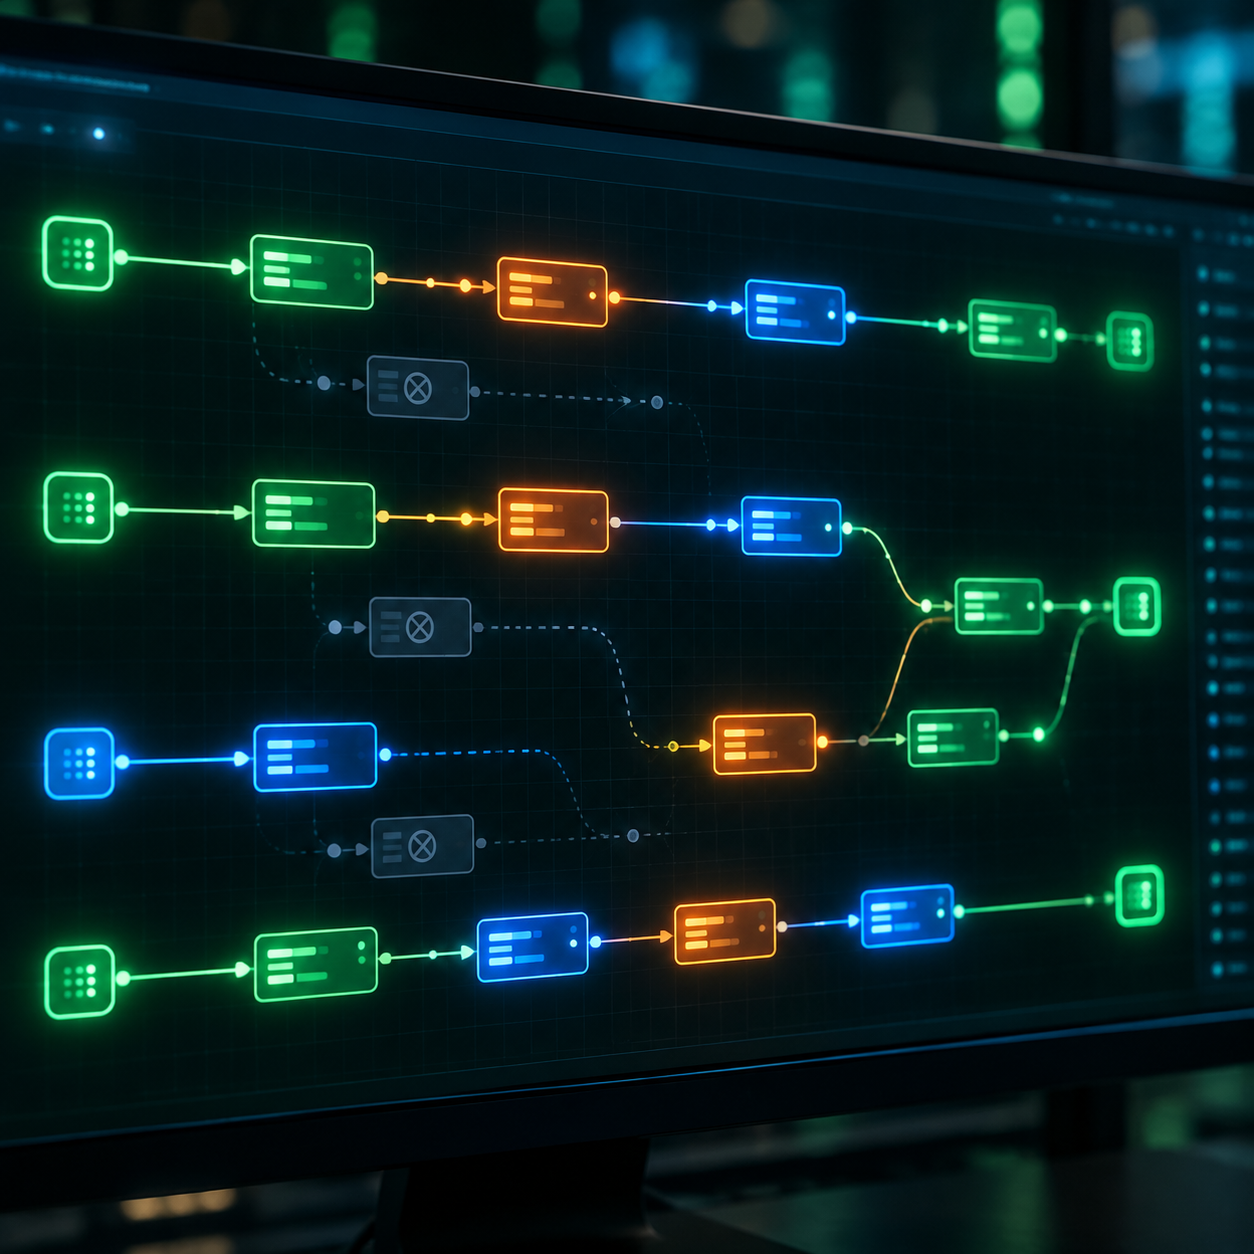
ProxyChains is a standard command-line utility that redirects application traffic through a chain of SOCKS or HTTP proxy servers.
First, open the application's primary configuration file:
sudo nano /etc/proxychains4.conf
Within the configuration file, select the appropriate operation mode:
- dynamic_chain: Traffic traverses proxies in the order specified. If a proxy in the list goes down, the system automatically skips it and forwards to the next link.
- strict_chain: Requires all proxies in the list to be operating properly. Traffic will be dropped if any link loses its connection, ensuring the absolute integrity of the security chain.
- random_chain: The system randomly selects servers from the configured list for each connection session.
Next, scroll to the bottom of the file to declare the list of intermediate servers under the ProxyList section:
[ProxyList]
# type  host            port    user    password
socks5  192.168.1.10    1080
http    203.0.113.15    8080    user1   pass1
socks5  198.51.100.22   1080
After saving the file, you can run any network command through the chain by prefixing it with proxychains.
Method 2: Setting Up Chains via SSH Tunnels
Leveraging the local port forwarding and dynamic forwarding capabilities of OpenSSH is another secure, reliable method to build nested proxy connections.
- Establish an encrypted connection to the first intermediate server:
ssh -D 1080 -N -f [email protected] - Configure the ~/.ssh/config file to route the connection for the second server through the newly opened local port on the first server:
Host proxy2
    HostName proxy2.example.com
    ProxyCommand nc -X 5 -x 127.0.0.1:1080 %h %p
Then, open a second dynamic tunnel through this connection. When data is sent to the new port, it will be automatically routed through both SSH server layers independently.
Challenges and Performance Considerations
Although proxy security is substantially reinforced when using multi-hop forwarding, operators must carefully consider the trade-offs:
Increased Network Latency
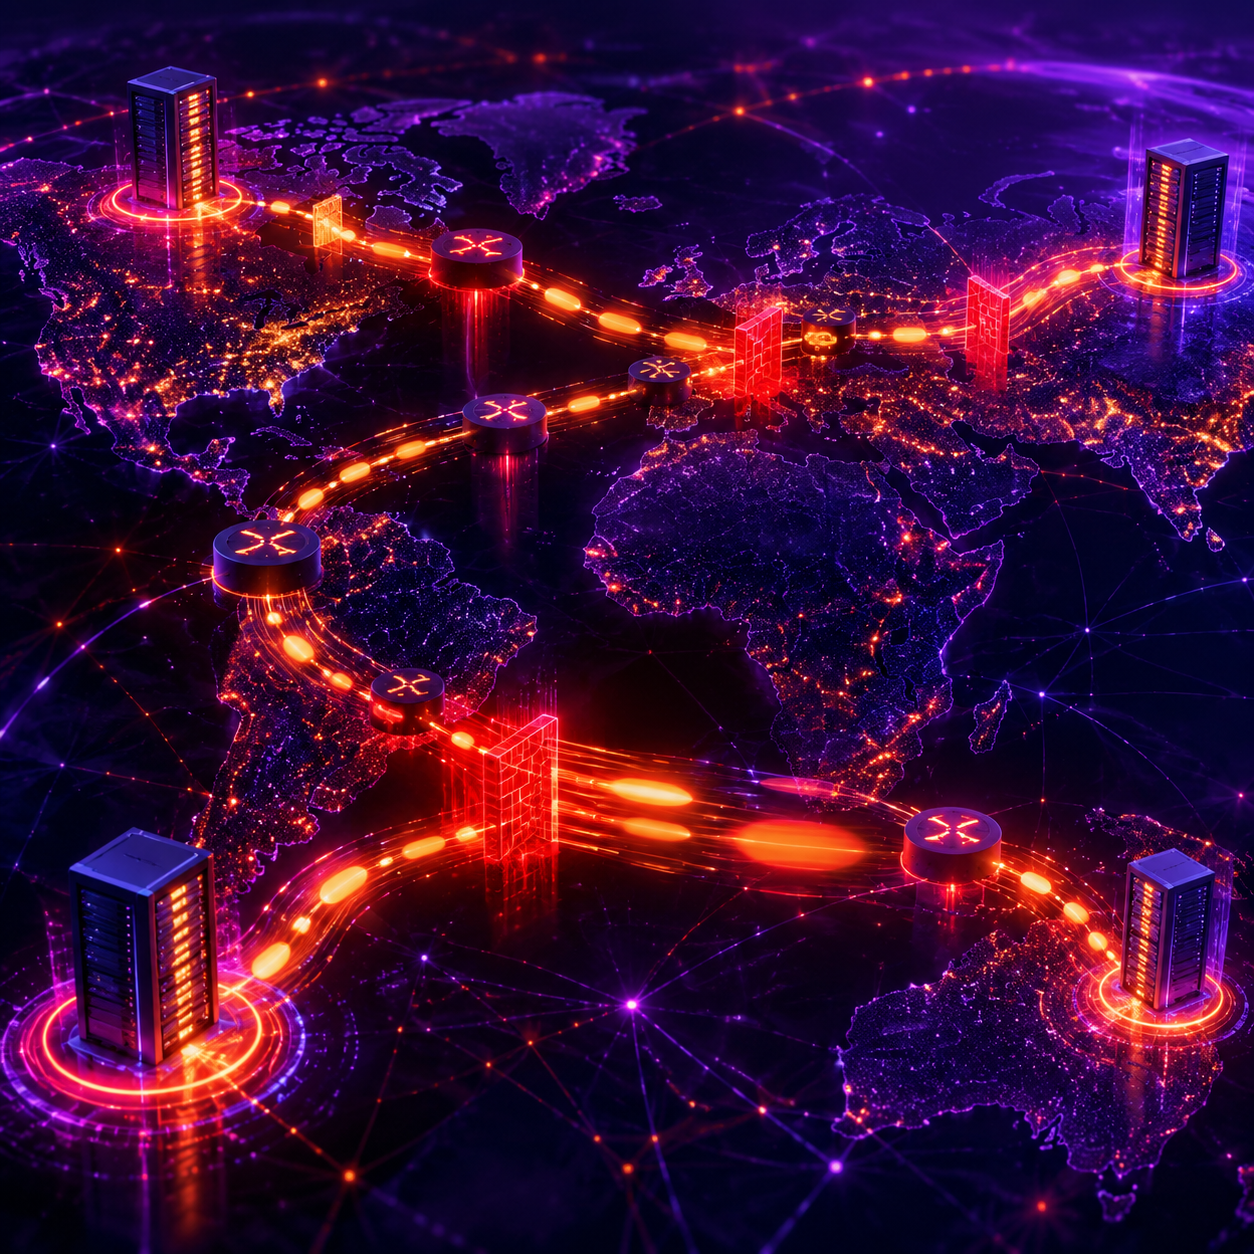
Each intermediate node in the chain means packets must travel an additional physical distance and undergo packet encapsulation/decapsulation. This increases overall connection latency, making it unsuitable for services requiring real-time responsiveness, such as VoIP or live video streaming.
DNS Leak Issues
A complex proxy chain can still expose identity if domain name resolution (DNS) queries are sent directly through the local Internet Service Provider's network port instead of being encapsulated within the chain. Always enable remote DNS resolution in your routing tool.
Overall System Reliability
The stability of a chain depends on the node with the lowest connection quality. If unreliable links are used, overall traffic may face frequent interruptions, disrupting continuous workflows.
Conclusion
Configuring proxy chaining is an effective technical solution that enhances information security, segregates identities, and facilitates secure traffic routing across tightly controlled network environments. For optimal results, administrators should select suitable protocols, rigorously manage the risk of DNS leaks, and balance security requirements against actual connection performance.
Related articles
Ready for real proxies, not just the guide?
Buy Residential, ISP, Datacenter, or Mobile proxies — live in minutes.
View products