
Hướng Dẫn Sử Dụng
Guide to System-Level Proxy Configuration for Docker Containers to Build Images and Fetch Packages Smoothly

Table of contents
The Importance of Proxy Configuration for Docker Environments
In enterprise software development environments, networks are typically strictly protected behind internal proxy servers or firewalls. While this ensures network security, it creates a significant barrier for DevOps engineers using Docker. Basic operations such as pulling base images from Docker Hub, updating packages via operating system commands, or installing project dependencies can run into timeouts or host resolution failures.
Understanding connection routing and properly applying docker proxy configuration is a prerequisite for a smooth continuous integration pipeline. Docker operates on a client-server architecture, so a single network setting on the host machine will not automatically apply across all Docker components. You must clearly distinguish between three independent scopes: proxy for the Docker daemon, proxy for docker build, and http proxy docker container at runtime.
Distinguishing the Three Proxy Scopes in Docker Architecture
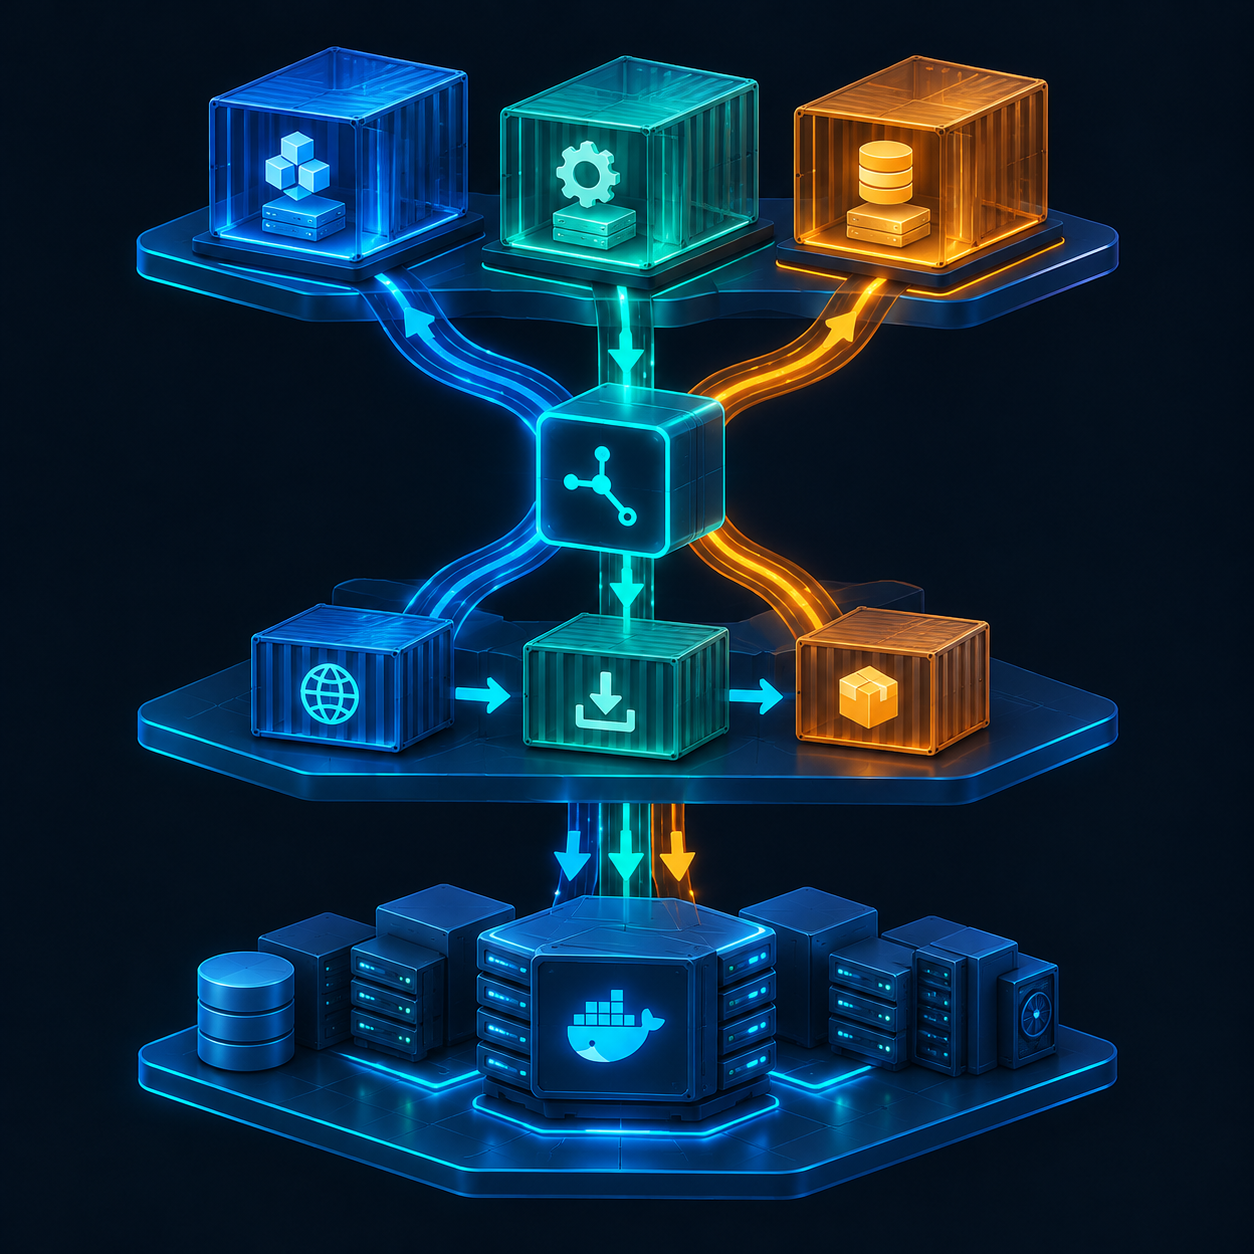
Many engineers encounter failed setups due to confusing Docker's network layers. Below are the three independent scopes that must be configured accurately:
- Docker Daemon (dockerd): Responsible for pulling images from public or private registries to the host machine. The proxy at this layer is configured through the system service.
- Image Build Process (docker build): Instructions in the Dockerfile, such as package installations, require an internet connection through a proxy passed via build arguments or client configurations.
- Running Containers (docker run): The runtime environment inside a container functions independently and requires separate proxy environment variables for internal applications to communicate externally.
Configuring Proxy for the Docker Daemon via systemd
When running an image pull command and receiving an error indicating an inability to connect to the remote host, the primary cause is that the Docker daemon is unaware of the proxy. Because the Docker daemon is managed by systemd on most Linux distributions, you need to modify its service configuration files.
Step 1: Create an Override Configuration Directory
Create a dedicated configuration directory for the Docker service to prevent changes from being overwritten during OS package updates:
sudo mkdir -p /etc/systemd/system/docker.service.d
Step 2: Create the http-proxy.conf File
Create and open a new configuration file using a text editor:
sudo nano /etc/systemd/system/docker.service.d/http-proxy.conf
Add the environment variable definitions for HTTP, HTTPS proxies, and the proxy bypass list:
[Service]
Environment="HTTP_PROXY=http://proxy.example.com:8080"
Environment="HTTPS_PROXY=http://proxy.example.com:8080"
Environment="NO_PROXY=localhost,127.0.0.1,docker-registry.internal"
Note: The NO_PROXY value is critical to ensure that the daemon does not route requests through the proxy when accessing internal registries or local network services.
Step 3: Reload Configuration and Restart the Service
Apply the changes by reloading the systemd configuration and restarting the Docker daemon service:
sudo systemctl daemon-reload
sudo systemctl restart docker
Verify whether the environment variables have been recognized by checking the Docker system info command and locating the HTTP Proxy section.
Setting Up Proxy Configuration for Docker Build
When building images, instructions that fetch packages from external repositories—such as OS package managers or language-specific package registries—will fail without an internet connection. There are two main approaches to resolve this issue.
Method 1: Using Build Args
This is a flexible approach applicable to individual build commands without altering default system configurations. You pass the arguments directly into the command:
docker build --build-arg HTTP_PROXY=http://proxy.example.com:8080 --build-arg HTTPS_PROXY=http://proxy.example.com:8080 --build-arg NO_PROXY=localhost,127.0.0.1 -t my-app:latest .
The advantage of this method is explicitness; however, the downside is that proxy parameters may inadvertently be persisted in the image metadata history if not handled carefully.
Method 2: Configuring Docker Client's config.json
In modern Docker versions, you can configure a default proxy for both the build process and container runtime via the client configuration file on the host. This file is located at ~/.docker/config.json.
Open or create the file and add the proxies configuration block:
{
"proxies": {
"default": {
"httpProxy": "http://proxy.example.com:8080",
"httpsProxy": "http://proxy.example.com:8080",
"noProxy": "localhost,127.0.0.1"
}
}
}
Once configured, the Docker client will automatically inject the corresponding proxy environment variables every time you run docker build or spin up a new container, without requiring manual parameters.
Configuring HTTP Proxy for Running Docker Containers
For active containers that need to access public APIs or external databases through a proxy, you can apply one of the following solutions.
Passing Environment Variables Directly via docker run
Use the -e flag to pass standard environment variables to the container:
docker run -d -e HTTP_PROXY="http://proxy.example.com:8080" -e HTTPS_PROXY="http://proxy.example.com:8080" -e NO_PROXY="localhost,127.0.0.1" my-app:latest
Declaring in Docker Compose
If you deploy multi-container applications using Docker Compose, maintaining the configuration within the compose file is optimal for environment consistency:
version: '3.8'
services:
app:
image: my-app:latest
environment:
- HTTP_PROXY=http://proxy.example.com:8080
- HTTPS_PROXY=http://proxy.example.com:8080
- NO_PROXY=localhost,127.0.0.1
Handling Proxies for Specific Package Managers Inside Containers
Although standard system environment variables are respected by most applications, some language package managers or OS utilities still require specific configuration files inside the Dockerfile to operate reliably.
Configuring OS Package Managers
Certain Linux distributions require declaring proxy settings inside the package manager's internal configuration file. For instance, on Debian or Ubuntu-based distributions, you can create a temporary configuration file before running installation commands:
RUN echo 'Acquire::http::Proxy "http://proxy.example.com:8080/";' > /etc/apt/apt.conf.d/proxy.conf
Configuring Development Tools
Tools like Git, Python package managers, or Node.js sometimes bypass system environment variables when encountering SSL certificate issues or proxy string formatting problems. Make sure to include the appropriate settings in your environment configuration workflow to ensure smooth package fetching.
Important Security and Operational Considerations
When deploying docker proxy at scale, engineers should keep the following security aspects in mind:
- Avoid hardcoding credentials in images: Never store proxy server usernames and passwords directly in a Dockerfile. If the proxy requires authentication, use secure mechanisms like BuildKit secret mounts.
- Configure NO_PROXY carefully: Ensure all internal subnets, Docker daemon network domains, and interconnected cluster services are included in the bypass list to prevent connection slowdowns or outages for internal traffic.
- Manage SSL/TLS Certificates (CA Certificates): If the proxy server performs deep packet inspection (SSL Inspection), processes inside the container may fail due to certificate errors. In such cases, you must copy the internal root CA certificates into the container's trusted certificate store before fetching packages.
Conclusion
Setting up the proper docker proxy configuration is a crucial initial step to eliminate troublesome network issues in enterprise environments. By cleanly separating the configurations across the Docker daemon, build processes, and container runtimes, you can effortlessly manage traffic flow, boost CI/CD pipeline reliability, and secure the entire software ecosystem.
Related articles
Ready for real proxies, not just the guide?
Buy Residential, ISP, Datacenter, or Mobile proxies — live in minutes.
View products